

Catch Design Flaws Before They Reach Code
By surfacing actionable guidance directly in the developer workflow, DevArmor keeps teams unblocked and aligned with secure design principles.


Guardrails that keep you shipping
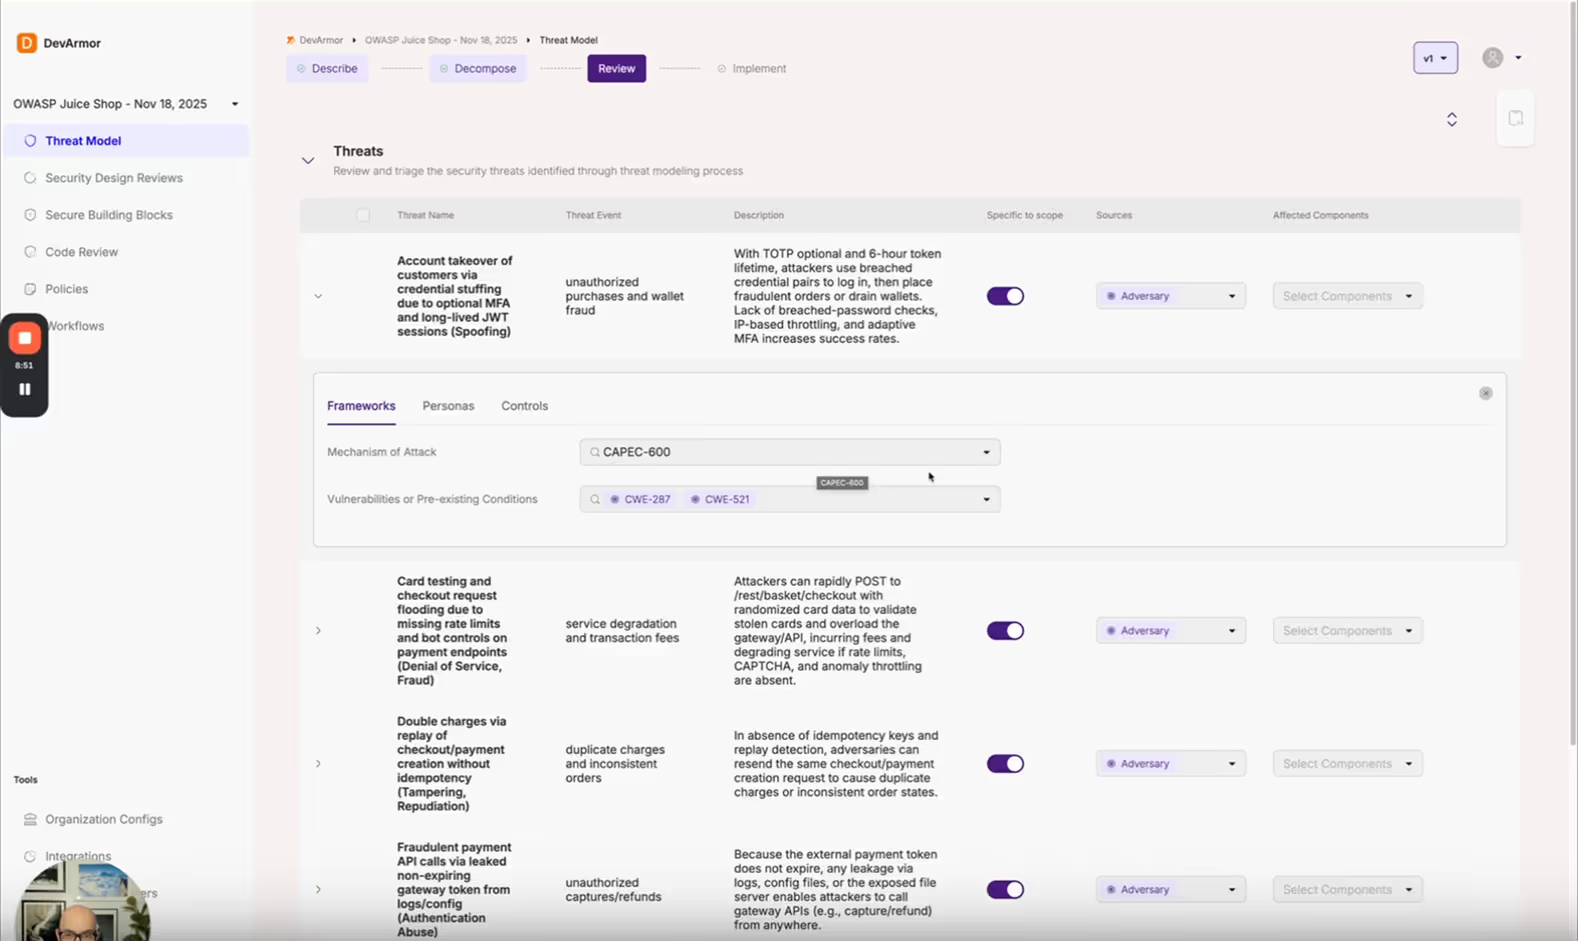
Every code change is reviewed for alignment with your architecture and security requirements, reducing rework and helping teams ship secure software faster.



 Reza Khosravi


 Amir Kavousian
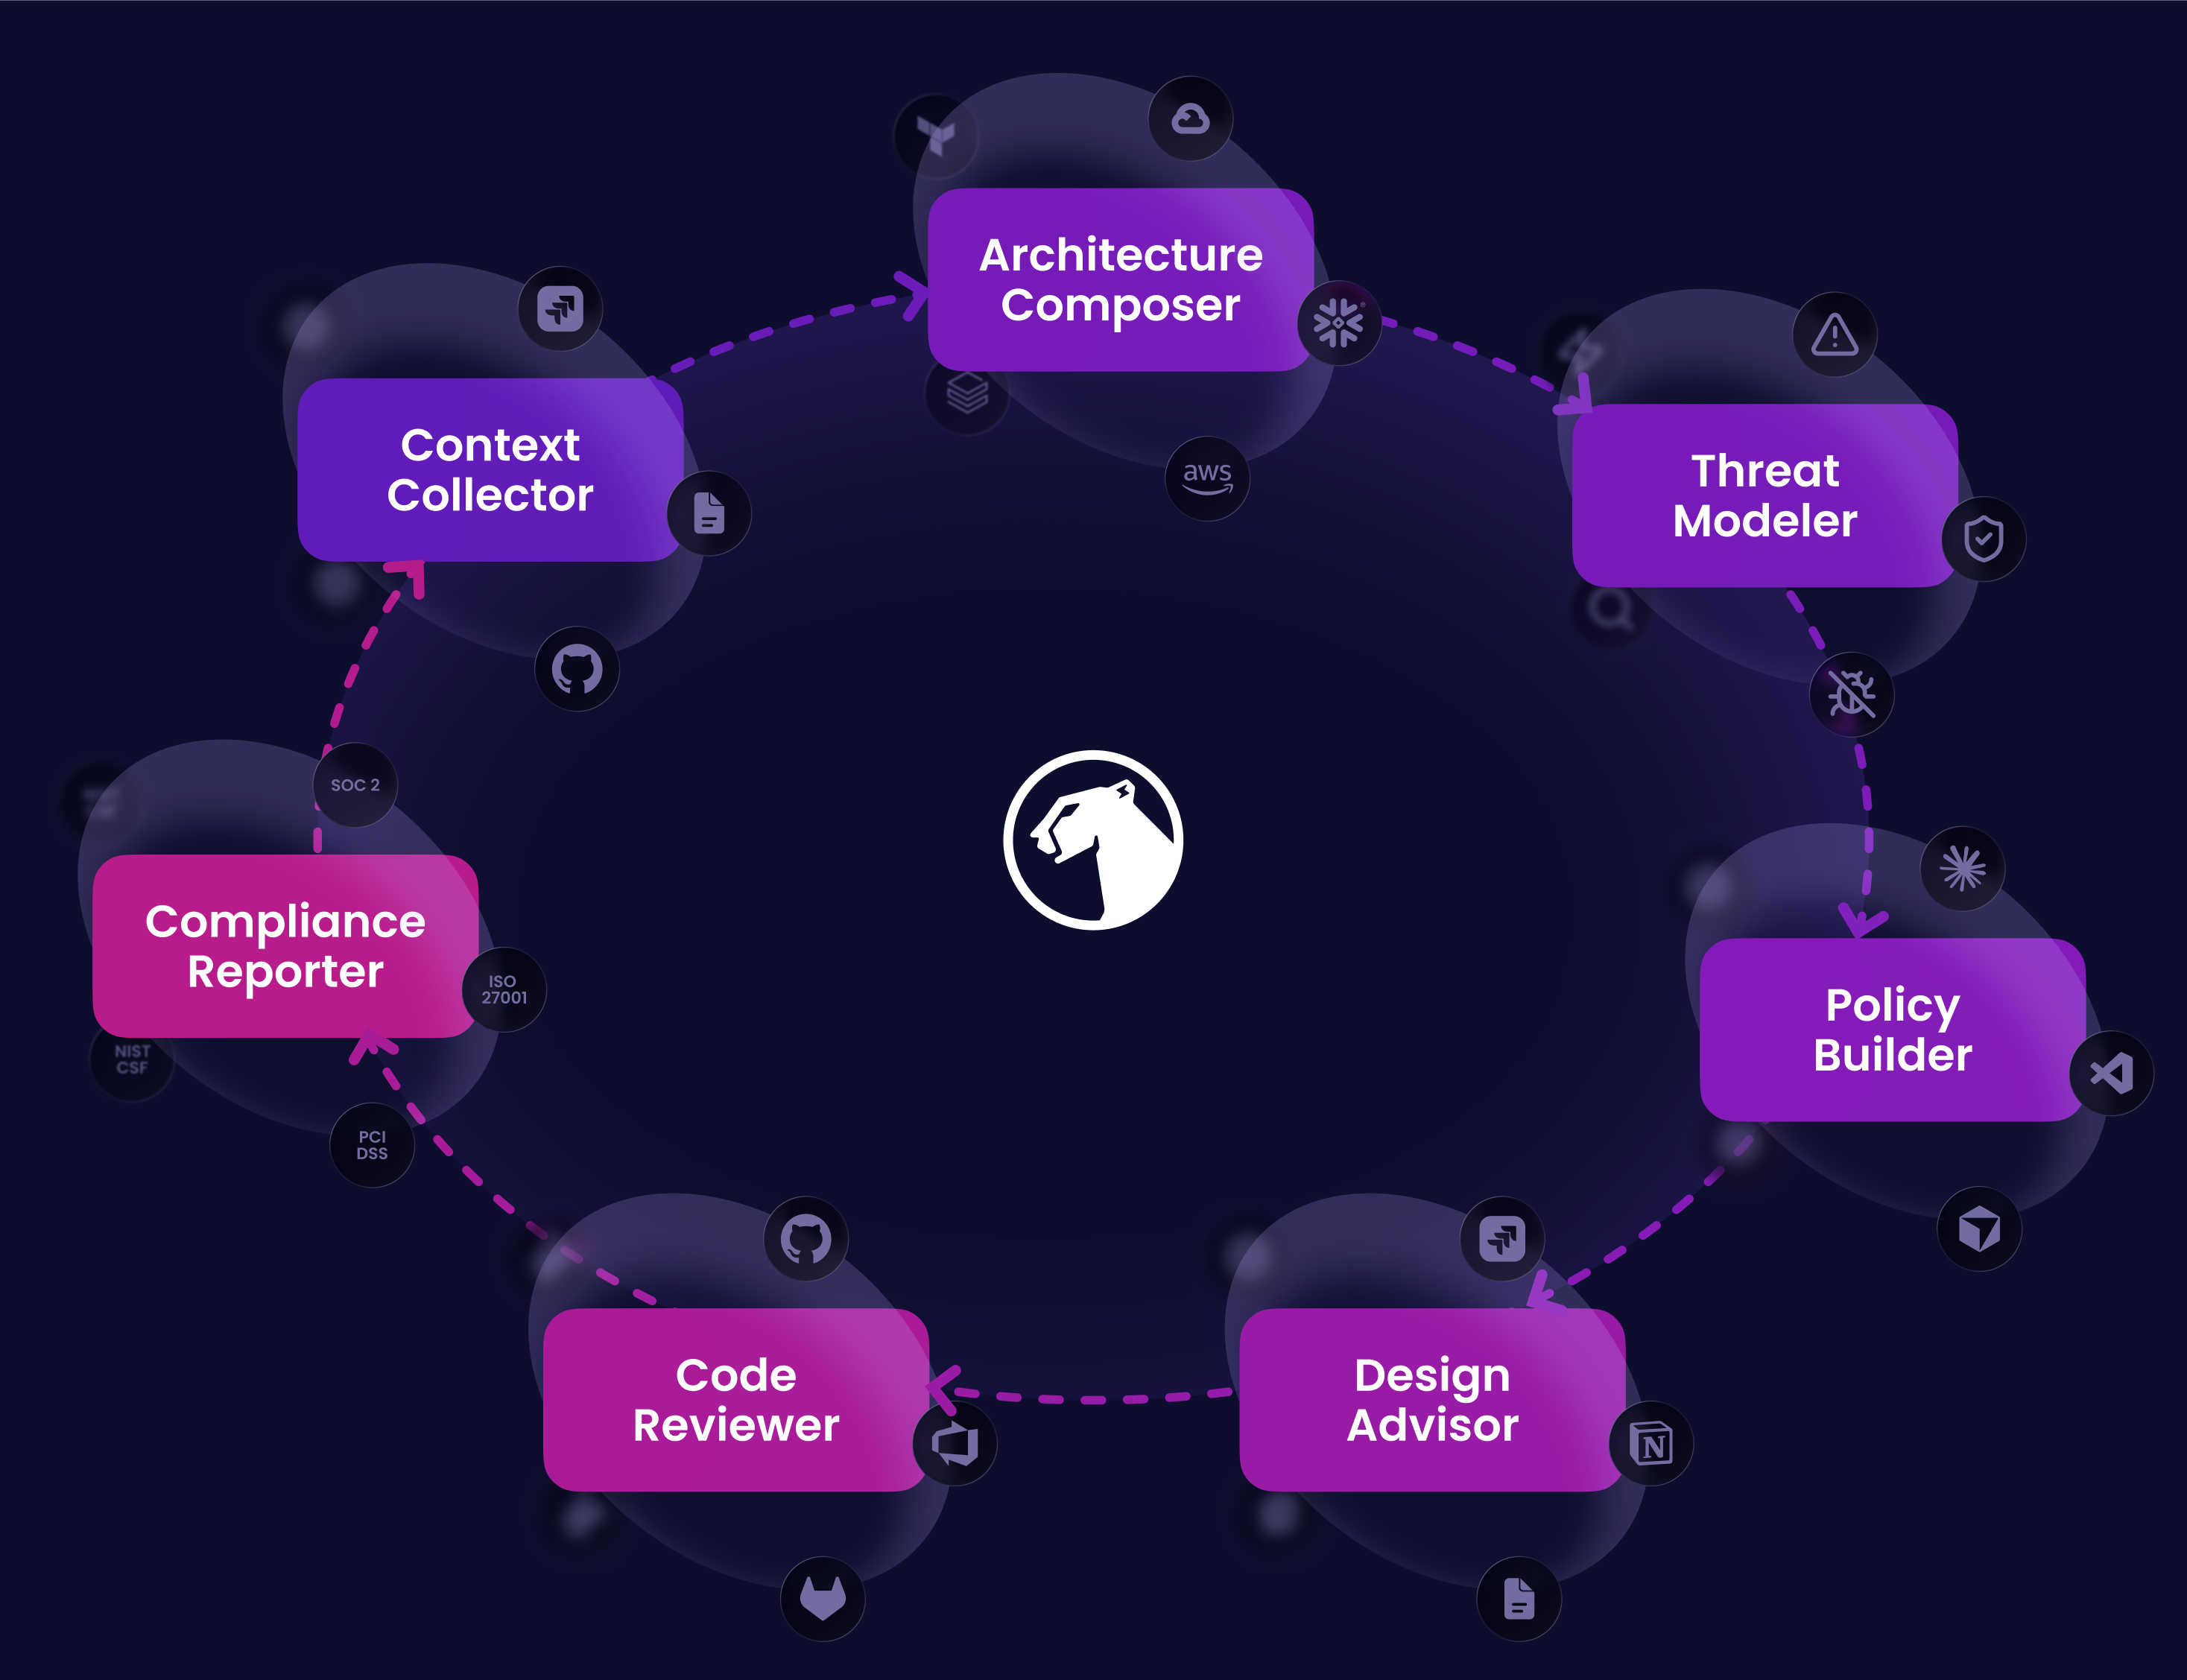
Every agent in DevArmor loop reads from the shared context and writes back to it. Nothing falls through the cracks. Every review, every policy, every enforcement decision, every exception becomes part of what the system knows about your organization, which makes the next decision faster, cheaper, and more precise.

 Amir Kavousian & Rami McCarthy
This article is co-authored with Rami McCarthy, Principal Security Researcher and prolific author of security blogs (ramimac.me). You can also find him on LinkedIn (linkedin.com/in/ramimac/).
 Reza Khosravi
The EU just made software defects and security flaws a product liability issue. Here's what changed and what it means for your team.
 Reza Khosravi
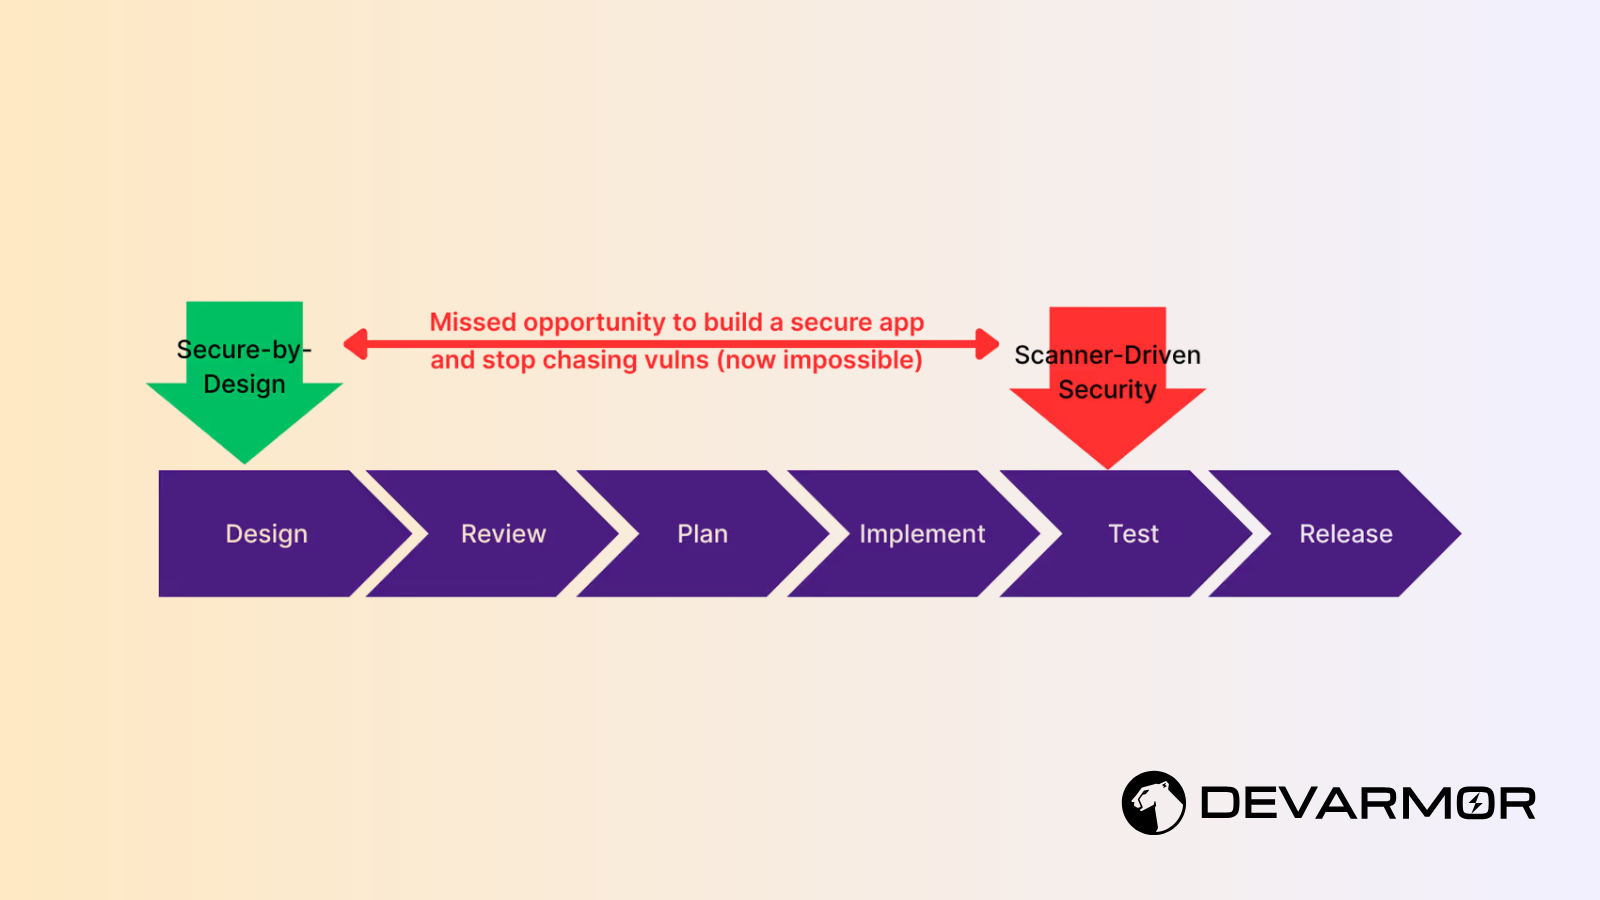
Where vulnerability management meets secure design.
 Amir Kavousian
AI can now generate working exploits from a CVE in under 15 minutes. Patching can't keep up. The only defense that moves faster than exploitation is the architectural decisions you made before the vulnerability existed.
 Petra Vukmirovic
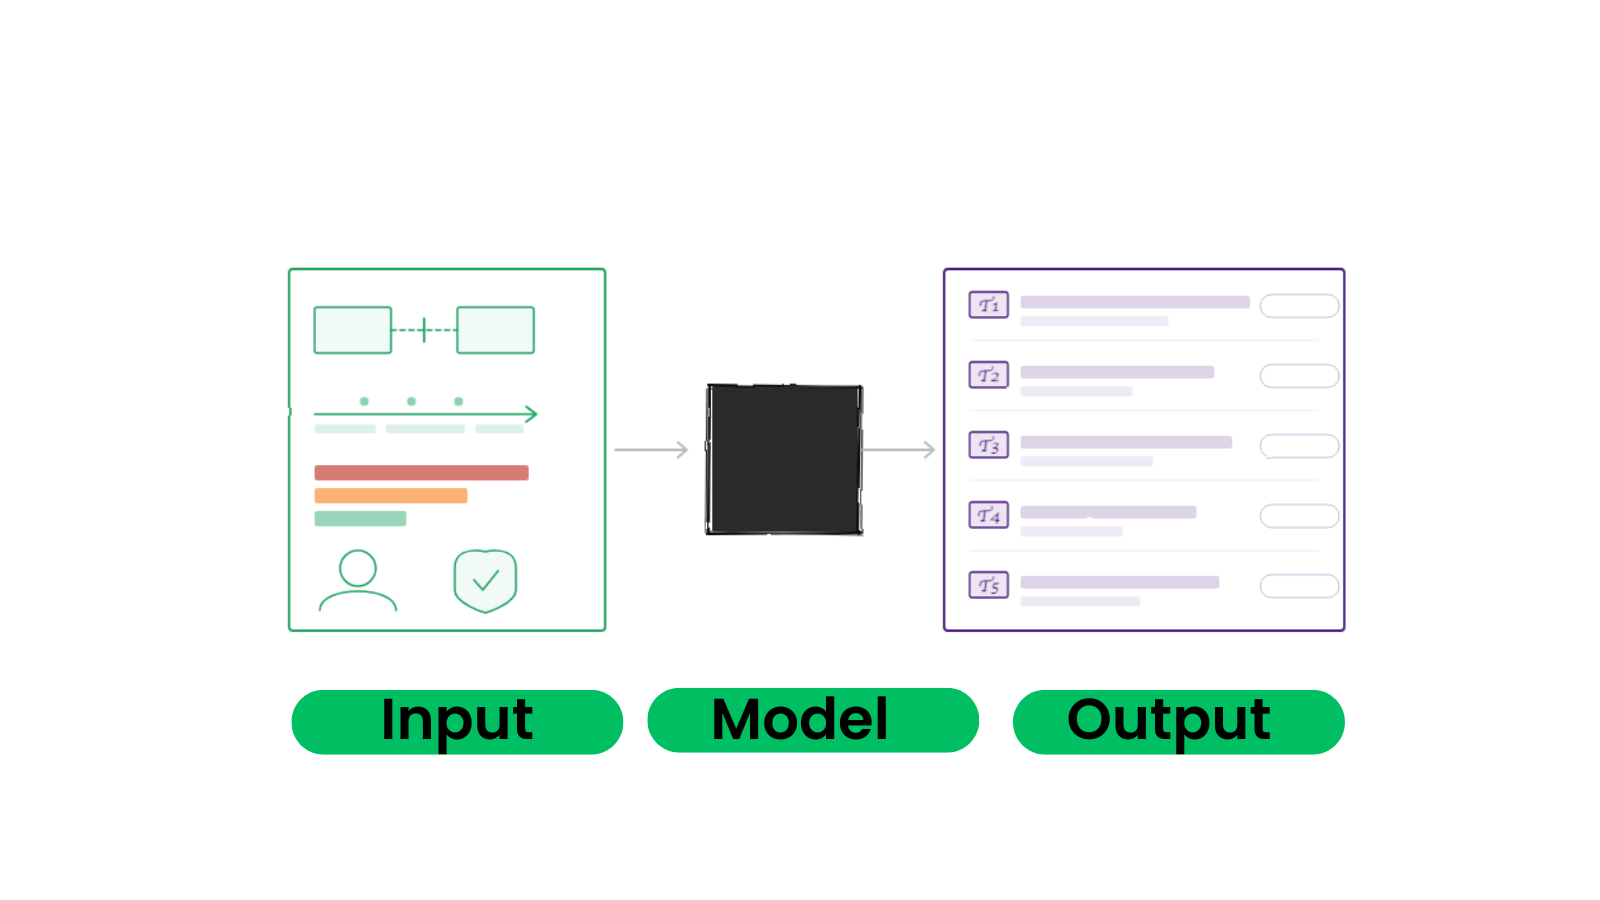
The practitioners who consistently produce good threat models are not the ones with the most sophisticated tooling. They are the ones who are obsessive about what goes in. Get that right, and the all the rest (the methodology, the AI assist, the output format ...) will fall into place.
 Amir Kavousian
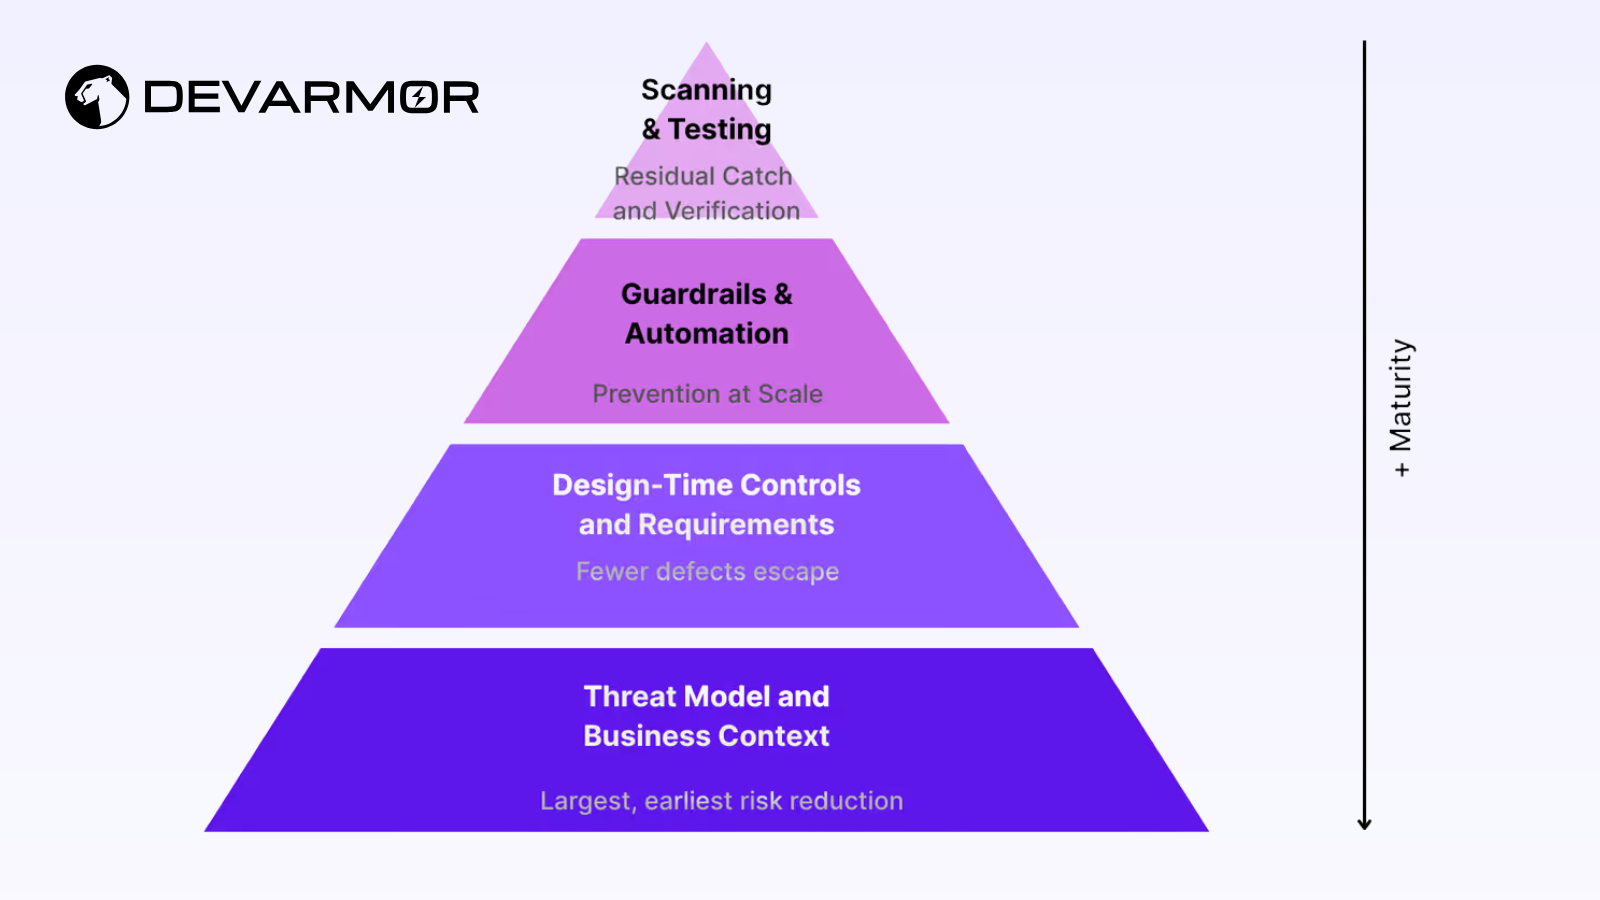
Early-stage security programs often measure success by the number of vulnerabilities closed. Mature programs measure it by how much risk actually goes down. Instead of treating every finding as equal, they weigh attacker intent, system exposure, and business impact, balancing technical severity (CVSS, EPSS) with architectural and operational context.

 Reza Khosravi
 Reza Khosravi

 Amir Kavousian
The future of AppSec isn't about chasing bugs or triaging alerts. It's about capturing intent, governing design, and enabling every contributor (human or AI) to build securely by default.
 Amir Kavousian
 Amir Kavousian
 Amir Kavousian